Hardware wallet maker Trezor says a breach at logistics provider ShipMonk exposed contact and order data for another approximately 67,000 U.S. customers after years-old records remained in the vendor’s systems despite written deletion assurances.
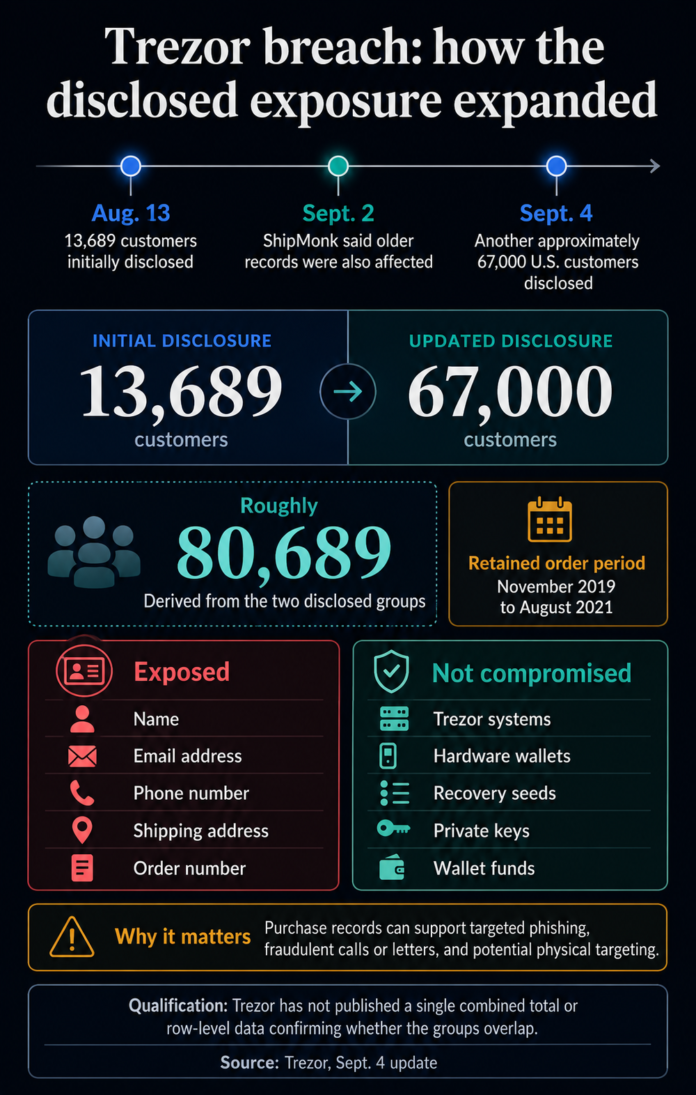
The Sept. 4 update expands an incident Trezor initially said affected 13,689 people. The two disclosed groups imply a total of roughly 80,689, although Trezor has not issued a single combined figure or published underlying data showing whether the groups overlap. Its use of “another” indicates that it considers the new records additional to the original cohort.
The newly disclosed records cover U.S. orders from November 2019 through August 2021 and include names, email addresses, phone numbers, shipping addresses and order numbers. The data can connect an identifiable person and physical location with a hardware-wallet purchase, creating risks beyond a conventional email leak.
Old data outlived a 90-day policy
When Trezor first disclosed the breach on Aug. 13, it counted 11,742 customers with full exposure and 1,947 with partial exposure. Trezor’s Aug. 13 account said older order data had already been deleted. An Aug. 14 clarification acknowledged that some partially exposed records included older orders.
The Sept. 4 update reverses that understanding. Trezor said it repeatedly requested and received written assurances that ShipMonk had deleted the data, yet records from 2019 to 2021 remained. Trezor’s published delivery-data policy says customer details should be deleted from both its own and its fulfillment partner’s systems after 90 days, with exceptions for ongoing order issues. The assurance letters and their dates have not been made public.
BleepingComputer reported that a ShipMonk notification attributed the original unauthorized access to a vulnerability in analytics platform Metabase. Metabase said the August zero-day could create a session tied to an administrator account and allow bulk table downloads. Once the provider incident was reassessed, the retained historical data expanded the number of Trezor customers known to be exposed.
The breach did not reach Trezor’s wallet systems. The company said its systems, products and services were not compromised and its devices remained secure. The listed exposed fields were contact and order data, not recovery seeds, private keys or wallet funds.
The risk instead sits around the wallet. Trezor warned that the information could support convincing scam emails, fraudulent calls or letters and potential physical targeting. Its Sept. 4 update did not identify a confirmed downstream attack caused by this dataset, so those outcomes remain risks rather than documented consequences.
Trezor said it emailed every newly affected customer directly and that anyone who did not receive its incident notice was not affected. It urged customers never to share a wallet backup or enter it on a website.
For hardware-wallet owners, the episode shows that protecting keys does not erase the purchase trail created by fulfillment. A deletion policy offers little protection if a vendor’s compliance is not verified.