Injective, a layer-1 blockchain network, produced no new block for nearly four hours during an emergency response to an exploit that researchers traced into core modules.
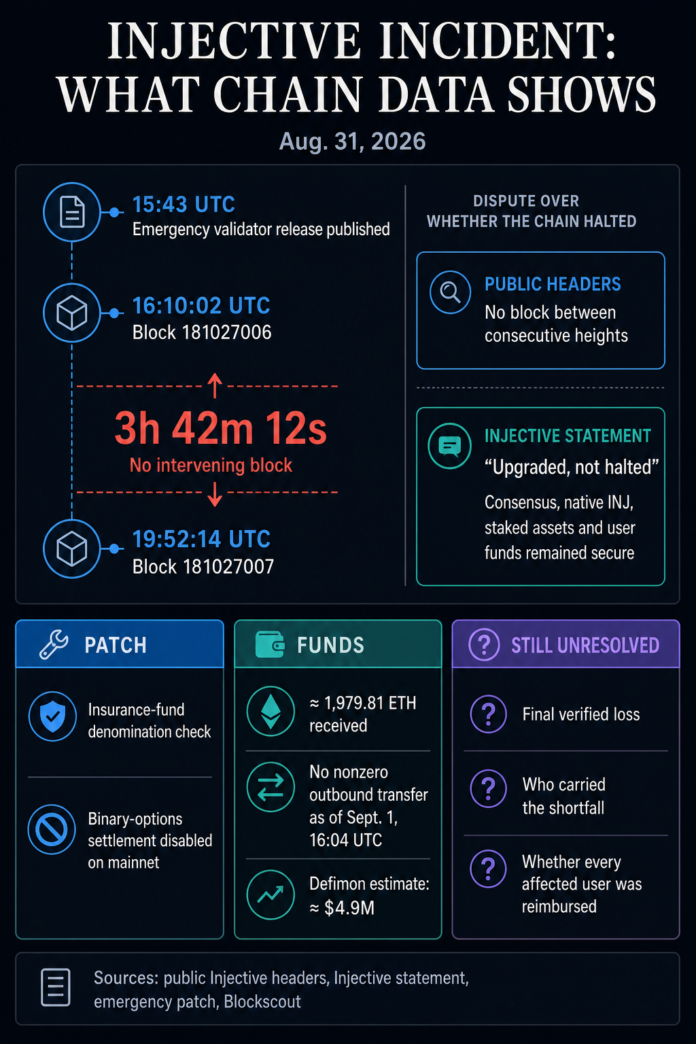
On Sept.1, the foundation said the blockchain was “upgraded, not halted” and that its consensus, native INJ, and staked assets were never compromised. It described the attack as affecting a small number of ecosystem applications using binary-options markets.
On-chain researcher Earthling Paddy challenged both characterizations, while crediting Injective for containing the exploit and keeping staked funds safe.
The ledger shows block 181027005 at 16:09:59 UTC on Aug. 31 before block production stopped for roughly four hours. Paddy said one earlier block alone took about 37 minutes, while infrastructure provider QuickNode also reported a stalled block height during the incident.
Injective said the accelerated upgrade took longer than expected as validators and ecosystem infrastructure moved to the emergency release. Some validators were temporarily jailed after missing the required upgrade window, while exchanges including Coinbase and Coins.ph temporarily restricted transfers.
Data from CryptoSlate shows INJ trading around $4.80 as of press time, down roughly 3% over the previous 24 hours.
Researcher disputes where the vulnerability sat
Paddy also questioned Injective’s description of the exploit as isolated to ecosystem applications.
He said the attack used messages from Injective’s native exchange and insurance modules, while the emergency v1.20.3-safeharbor.1 release patched the chain’s core code by adding an insurance-fund denomination check and disabling binary-options settlement on mainnet.
That would place the vulnerable logic inside a protocol module used by applications rather than solely within application code.
Injective has not yet published a full technical postmortem. Its statement said the relevant attack vector had been contained and patched and that the foundation was adding stronger invariants, real-time monitoring, and other safeguards.
Researchers estimate about $4.9 million was bridged to Ethereum during the exploit. Paddy said roughly that amount remained in the attacker-linked wallet and had not moved.
The final loss allocation remains unclear. Injective has not disclosed how much was ultimately drained, which party absorbed any shortfall, or whether an ecosystem pool that now appears replenished was restored by the foundation, developers, or another participant.
Instead, the blockchain has maintained that its users weren’t affected. In an X post, Injective CEO Eric Chen said:
“Injective users aren’t affected and we’ve been helping the team on recovery. Always sad to see exploits happening in the ecosystem but we’re glad that the incident was contained before further harm was done.”
Nonetheless, the incident therefore leaves two separate findings intact. Injective’s consensus and staked INJ were not compromised, while its emergency response still coincided with a multi-hour interruption in block production and required a core-code patch.