HP Wolf Security, the company’s threat-research team, said a fake AI crypto-trading assistant distributed malware that could replace browser crypto wallet extensions on an infected Windows computer and turn the familiar wallet interface into a credential trap.
The campaign appeared in HP’s September threat report, published Sept. 17 and based on threats observed from April through June 2026. HP described a compromise that began on a user’s endpoint after a counterfeit trading tool was downloaded and run, not a breach of Coinbase, MetaMask, or their official extensions.
Malwarebytes had documented the TradingClaw campaign in April and found that Needle Stealer also circulated through other malware loaders. The fake AI assistant was one route into a broader malware operation.
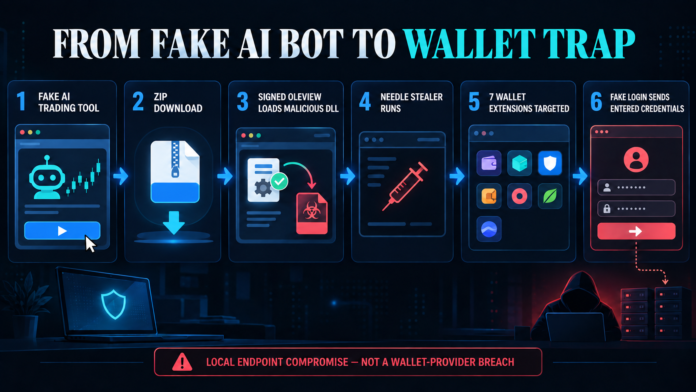
Attackers promoted tradingclaw[.]pro as an AI assistant that could follow a personalized strategy and trade around the clock, according to the full HP report. Search-engine poisoning and paid advertisements directed prospective victims to a ZIP file presented as the software’s installer.
The archive contained an executable named Trading Agent.exe and a DLL named iviewers.dll. HP identified the executable as OLEView, Microsoft’s legitimate, digitally signed OLE/COM Object Viewer. HP said the signed program helped bypass Microsoft’s SmartScreen reputation check, while the malicious payload remained in the accompanying DLL.
Running the trusted-looking program caused it to load that DLL. The code then decrypted Needle Stealer and used process hollowing, a technique that runs malicious code inside a newly launched legitimate process.
How the crypto wallet swap worked
Needle Stealer enumerated Chromium browser extensions and checked their 32-character IDs against a hardcoded list covering Phantom, Trust Wallet, Atomic Wallet, Coinbase Wallet, OKX Wallet, MetaMask, and Tonkeeper.
When it found a target, the malware shut down the browser and extracted a corresponding malicious extension into the existing extension folder.
On its first launch, the replacement connected to a command-and-control server used by the attacker and loaded backup domains. HP said the attackers had built realistic login screens, and a crypto wallet ID and password entered into a counterfeit interface could be sent to the operator.
MetaMask’s guidance says that, for crypto wallets created with a Secret Recovery Phrase, the password unlocks MetaMask locally and cannot restore the wallet elsewhere. Even so, the substituted extension was operating on an already compromised device, leaving locally accessible funds at risk.
Neither HP’s report nor its newsroom summary disclosed a campaign-wide victim count or aggregate crypto-loss figure, leaving the operation’s scale unknown.